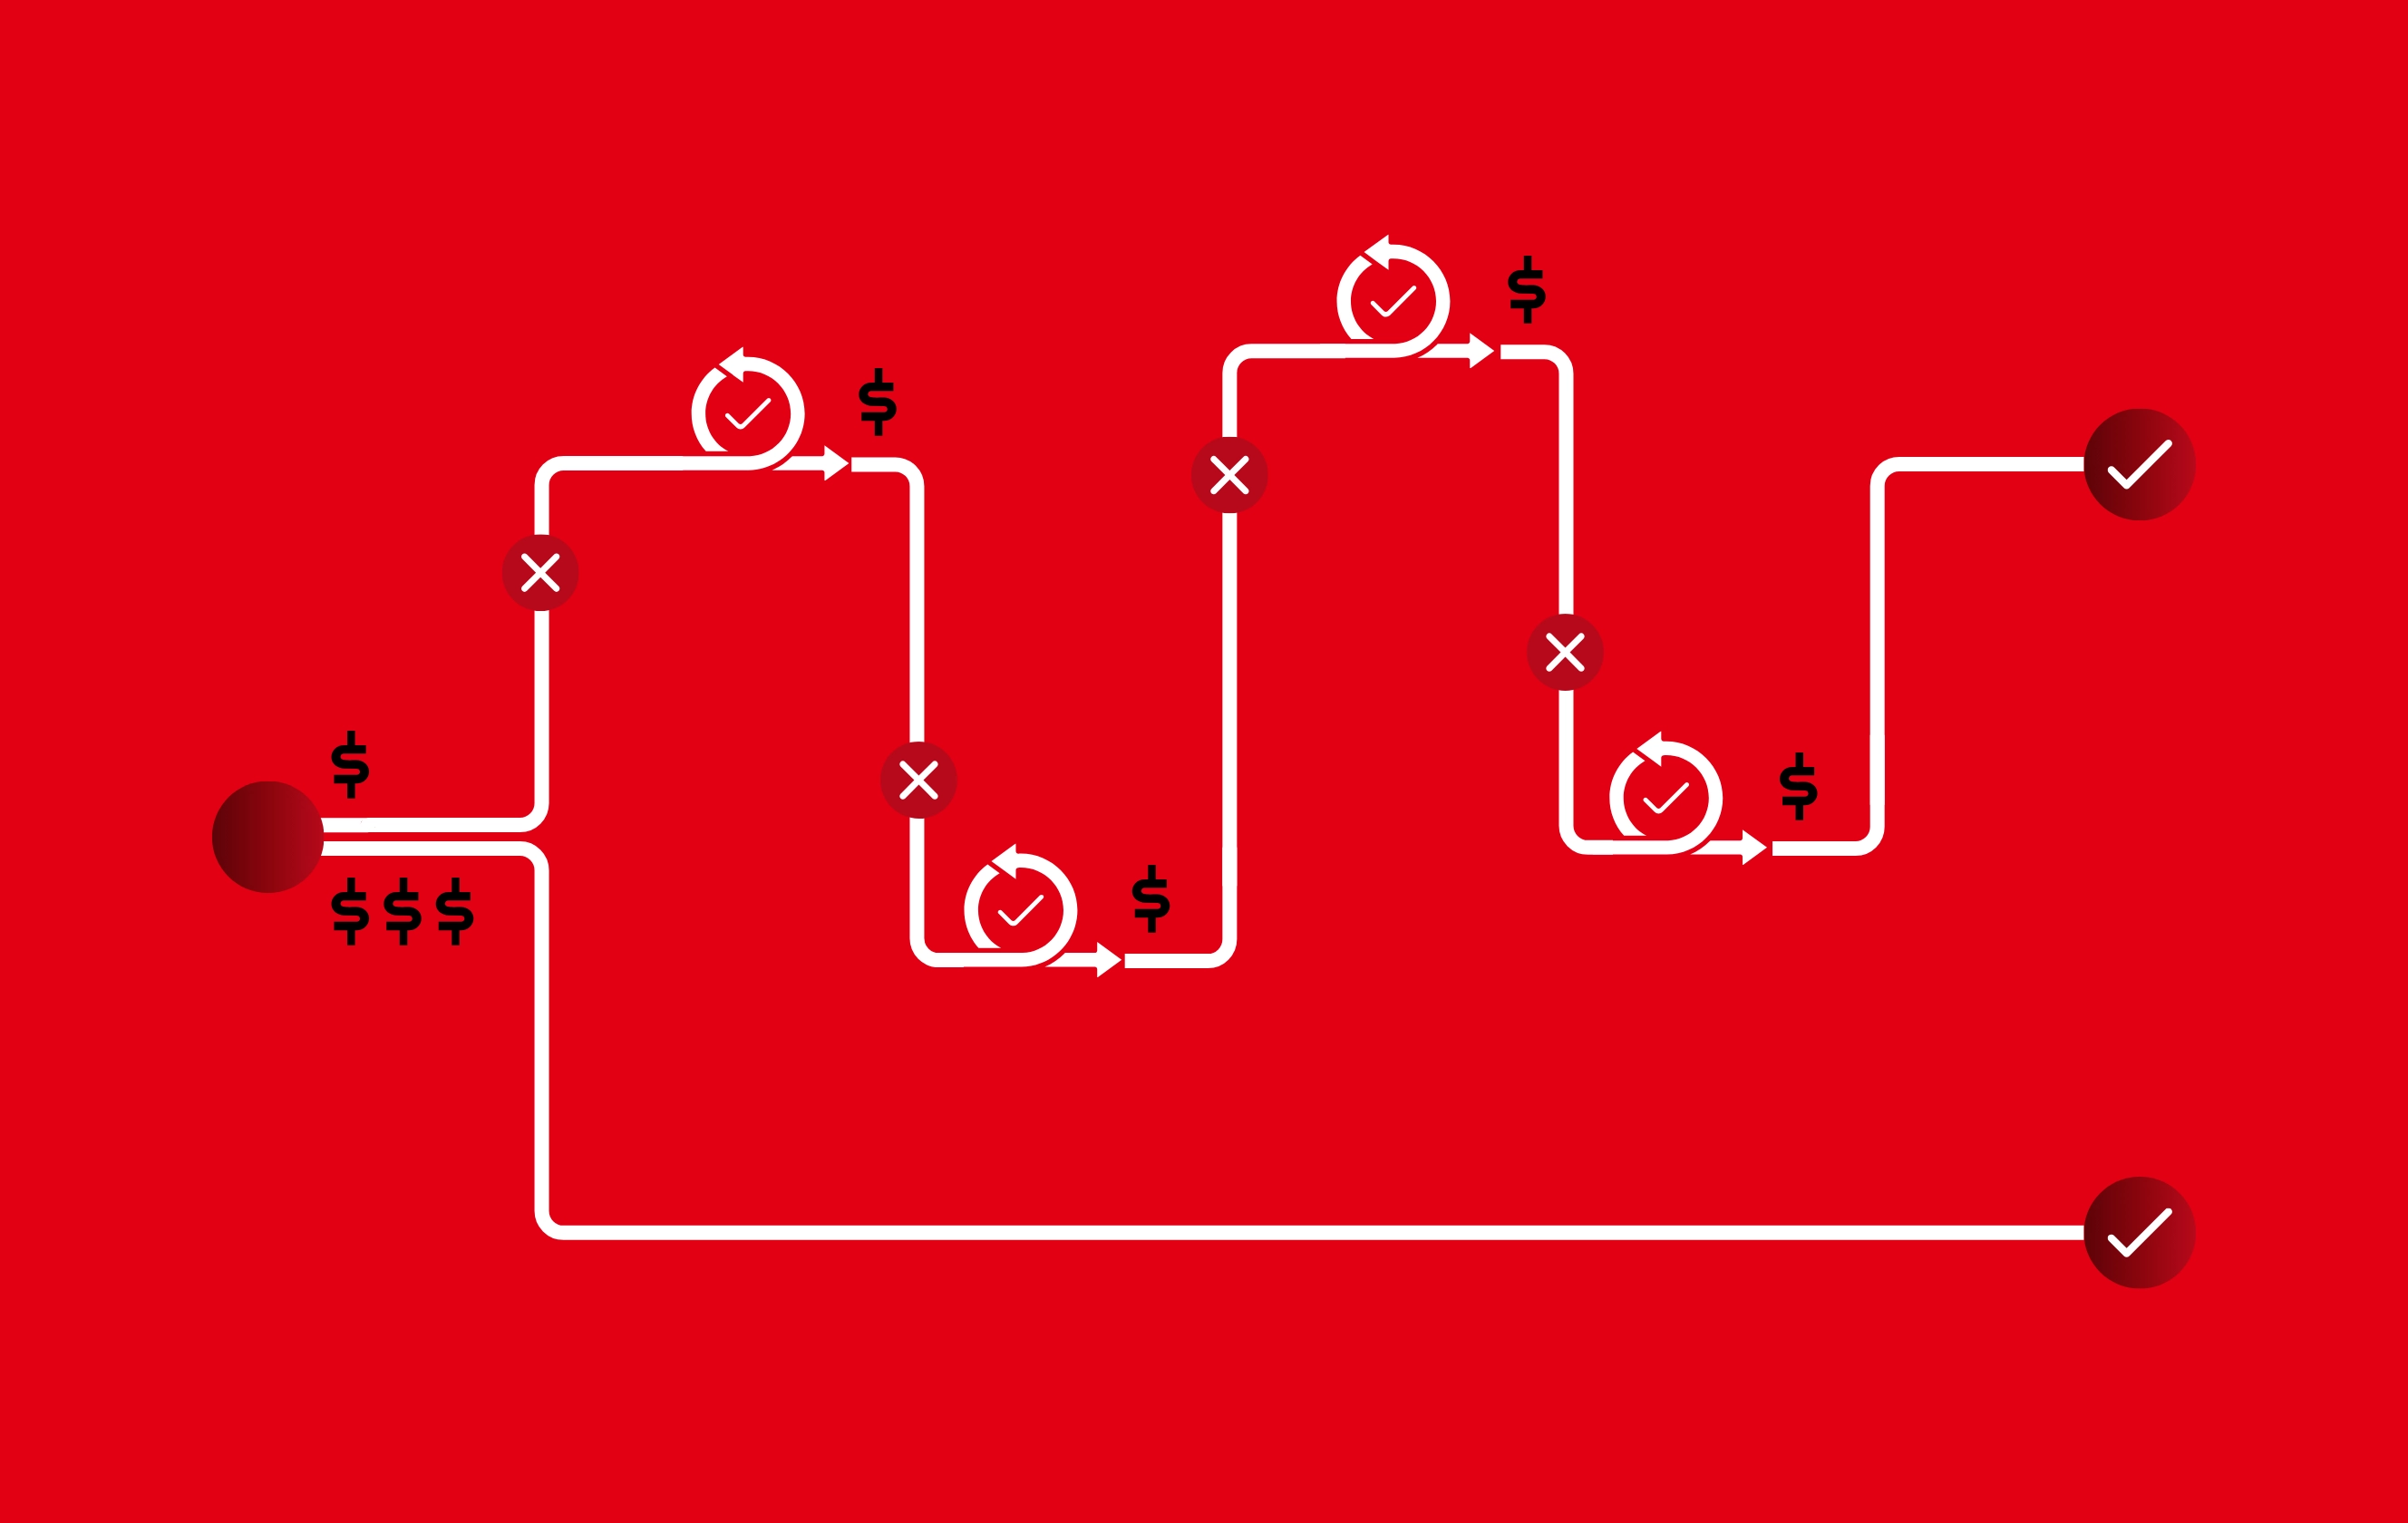
Enforce AI policy without slowing anyone down
Enforce budget and quality controls, access to models, and data policy across all your human and agentic builders, without locking anyone into a single provider or stack.
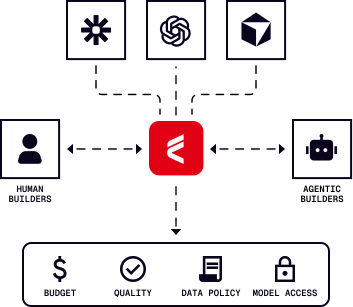
identity provider


US Bank


consulting firm


automation provider


Card Issuer

Every AI request is a policy decision, but nothing is checking it
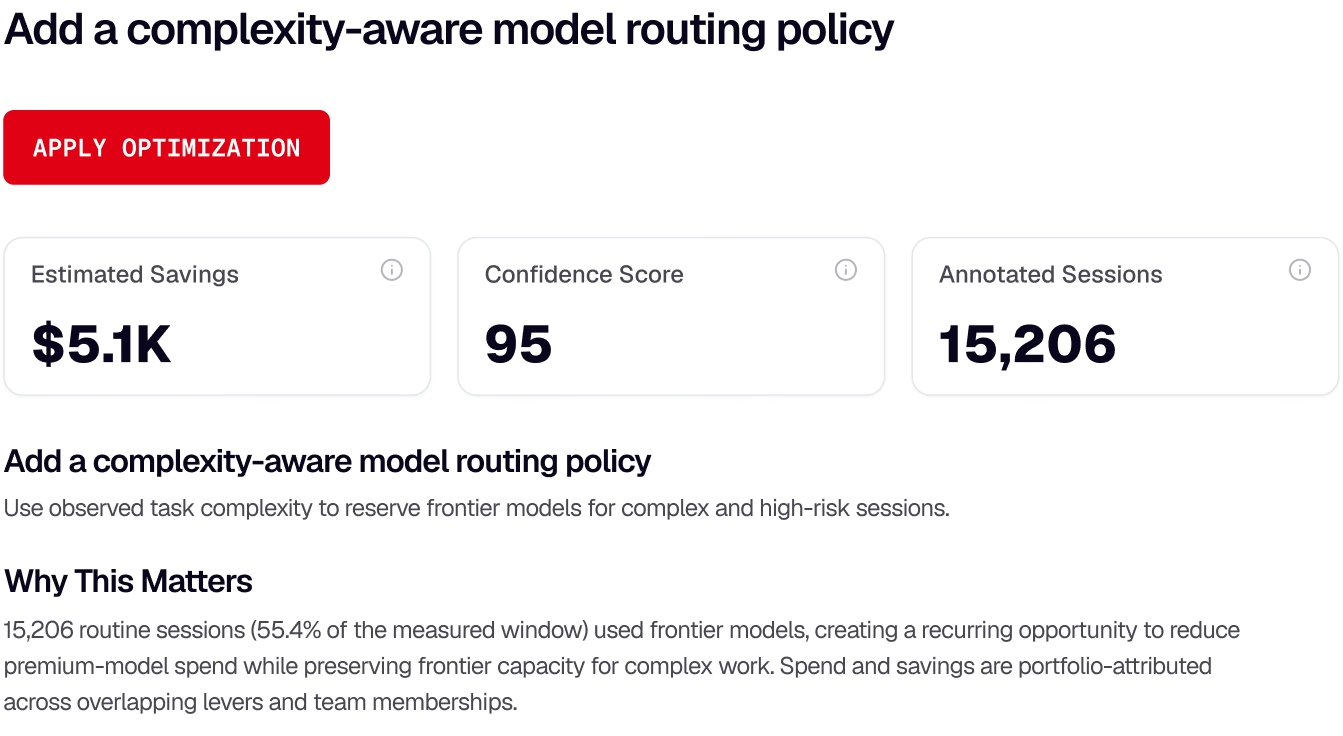
Each AI coding request picks a model and a tool, and every choice comes with a cost. That happens thousands of times a day, more and more often by agents with no human in the loop. In most organizations, nothing checks those choices against policy.

Defaults nobody chose
A flagship model runs routine work because it's the default, not because anyone proved it was the best route

Shadow usage
Builders and agents use models through tools and accounts that never went through security review

Unenforceable policy
An approved-model list in a wiki has no way to stop a request that simply
ignores it
Usage caps ≠ governance
When an AI bill comes in far higher than expected, companies often put a blanket usage cap on everyone. But a cap stops a thrashing agent and a developer shipping critical work at the same threshold.
Real AI governance enforces policy on model routes, leaves an audit trail, and turns approved decisions into real-time guardrails for AI coding work.
AI governance in place where the work actually happens
Faros records every AI session, enforces policy on every request, and keeps the evidence, across all harnesses, models, and routes your builders use. Guardrails replace usage caps, so your most productive teams are the last to be slowed down.
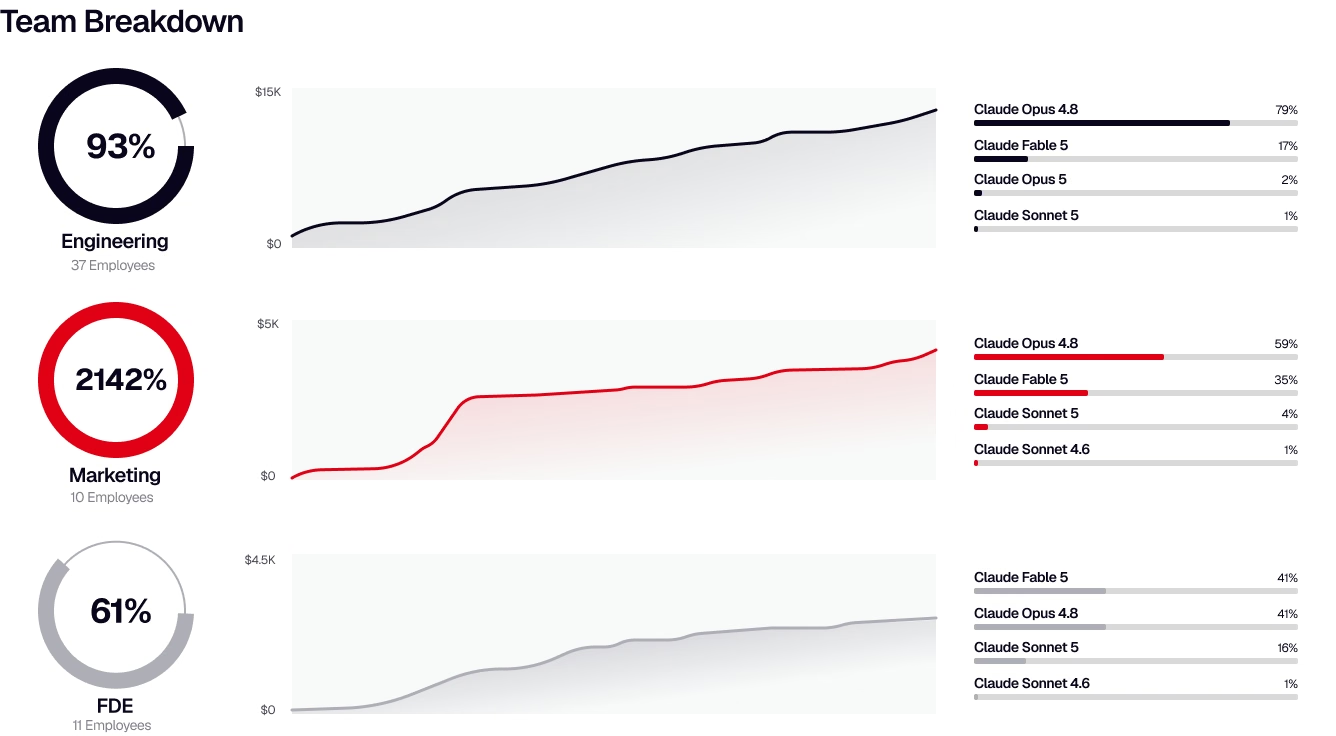
A clear view of what’s driving overspend
See which teams are trending over quota, and trace the overspend to the model and harness combinations behind it. Pinpoint which spend to protect and which to cut before the invoice arrives.
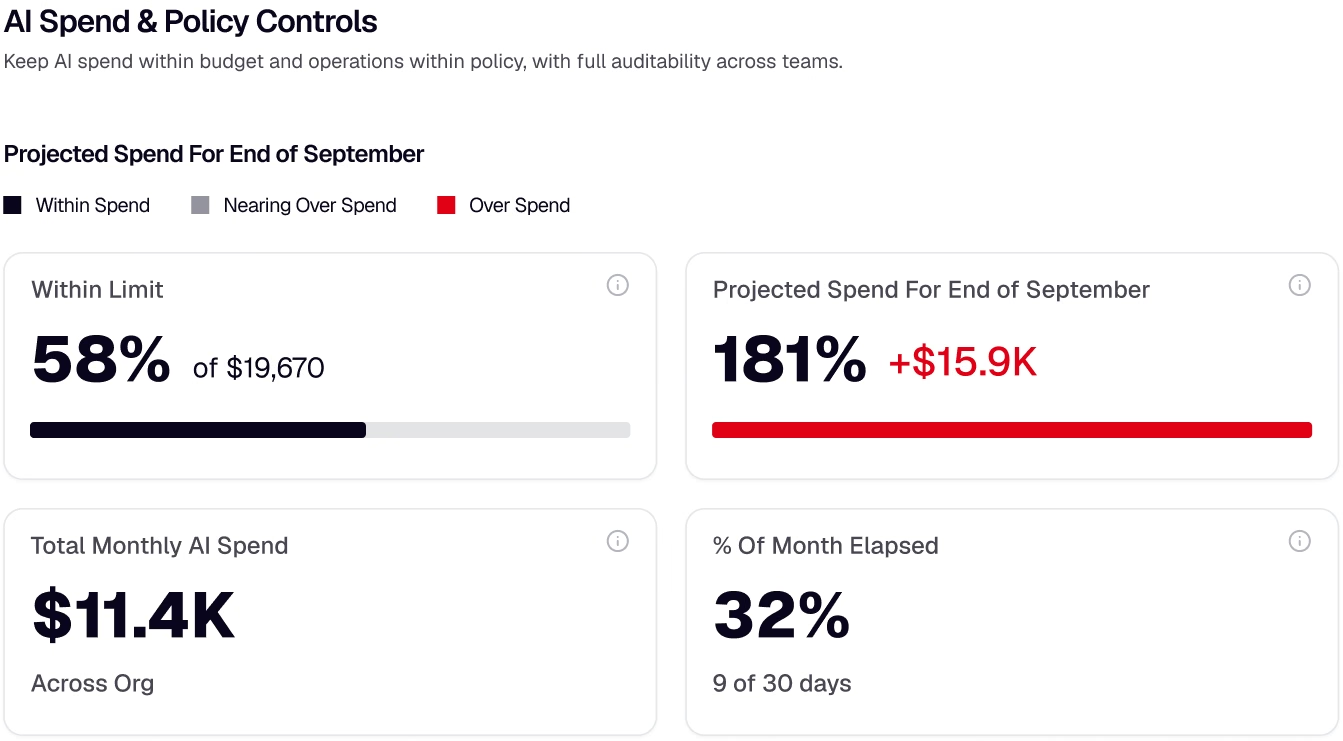
AI spend control by policy
Set quotas by team, project, or business unit, and choose what happens automatically as one nears its limit: throttle lower-priority work, switch to a cheaper model, or escalate for approval.
Policy enforced where the call happens
Set which models, harnesses, and configurations each team can use. Faros enforces that list in the request path, so unapproved models and unreviewed shadow AI tools never get through.
Already have a gateway? Faros can drive yours.
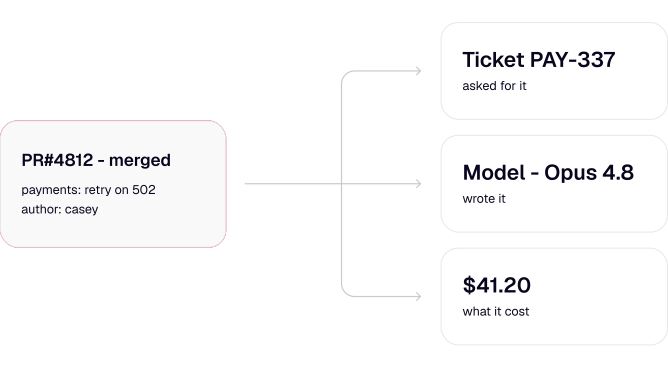
An audit trail you can hand off
Access a complete record of AI activity for a repo, a
team, or a time window: every session, the model
behind it, the policy in force, and what it cost.
Certified for SOC 2, ISO 27001, GDPR and CSA
STAR, and deployable as SaaS, hybrid, or on prem.
Top questions
Enterprise-grade security
Faros is built to enterprise-grade standards and is SOC 2 Type II, ISO 27001, and GDPR compliant. Your data never leaves your boundary. Learn more about security practices.



Find out what your AI has been doing
Bring your repo and a time window. We will show you the record: every session, the models behind it, the policy in force, and what it cost, then how to enforce the policy you actually want without slowing down your builders.
What’s new at Faros
The Speed Trap: 8 takeaways from our latest AI engineering research
AI made software development faster, but review gaps, QA bottlenecks, and rising incident volume reveal a new risk: the Speed Trap.